
-
Creating synergies through a culture of trust
Take a pinch of value-based compliance beginnings and a few standards-based compliance principles and we already have highly efficient compliance management for a company. In fact, both values and standards can strengthen a company's compliance management in a properly coordinated manner. Companies should therefore create a culture of trust and strengthen self-responsibility through compliance management. Values and standards should be in line with each other....
-
External rules and one's own morality
If a misconduct generally contradicts one's own morality and that of the environment, this can prevent wrong conduct. Values and rules that are commonly used in a society form morality. People see moral action as just and agree with it. Purpose of morality In a society, ethical and moral values control the conduct of people's lives. Morality...
-
Compliance Officer with Liability and Responsibility
With directors-and-officers insurance (directors-and-officers insurance, organ or manager liability insurance), a company can protect its compliance officer in the civil context. After all, the compliance officer is liable and responsible. A D&O insurance is a property liability insurance and belongs to professional liability insurance. The Chief Compliance Officer bears the highest liability risk. Lawyer Dipl.-Ing. Michael Horak, LL.M. Insurance A D&O insurance includes a company for its institutions...
-
Become a compliance officer with experience
Business administration, computer science, law – who wants to become a compliance officer creates a good foundation with a legal, business or information science degree. The more professional experience a compliance officer presents, the more salary he can demand. Lawyer Dipl.-Ing. Michael Horak, LL.M. Gain experience A compliance officer should be familiar with the company in which he wants to perform the function as a compliance officer....
-

Knowledge and skills of a compliance officer
Legal understanding, entrepreneurial understanding and security in the handling of data – these are the most important characteristics of a compliance officer. In addition, however, there is still further knowledge and skills that are among the requirements for a compliance officer. Strategic thinking is an ability that no compliance officer should lack. Lawyer Dipl.-Ing. Michael Horak, LL.M. We offer you a further education...
-
First Compliance Steps of a Compliance Officer
The first compliance steps of a compliance officer include the establishment of a compliance management system. For some companies, compliance is something completely new and they are just familiar with taking first compliance steps. Other companies have already established a fully-fledged compliance management system. We're professionals. Use a first compliance consultation. Compliance Analysis The compliance officer first deals with...
-
Internal Compliance Officer
The larger the company, the more comprehensive the compliance requirements. A single internal compliance officer can therefore be required quickly. Finally, compliance is branched out into all areas of the company where laws and regulations prevail. Already in the light of the existing regulatory density for companies and entrepreneurs, cross-border activities, increasing regulation and, in particular, special liability for management bodies, today...
-
Compliance Officer as an interface
As an interface between the specialist departments and the management, compliance officers take care of the optimal flow of information between the company management and the specialist areas. From the differentiated competences to the different requirements for confidentiality, the officer must therefore take a look at everything. We are compliance professionals and support your legal affairs. Maintain legal compliance To ensure smooth business operations and legal compliance...
-
Compliance managers are in demand
The demand for compliance managers is high. Qualified specialists in the area of compliance are constantly being sought. We're professionals. Use a first compliance consultation. Responsibility of the Compliance Manager As responsible for the legal conformity of all processes and business processes within a company, compliance managers are responsible for ensuring that the company's operations run in accordance with applicable laws and internal standards. The Compliance Manager actively monitors...
-
Death Sin 4: Governance Structure Missed
Although companies control basic processes and controls, our experience often lacks governance structure. A good governance structure is designed to ensure risk coverage as well as the adaptation of their processes and controls to regulatory requirements. We are happy to advise you in IT compliance. Effects of a lack of governance structure Impacts of a structurally-free compliance governance can be the following: The corporate architecture becomes sluggish. Reactions to...
Just call us. We are happy to advise you.
Legal, internal and contractual regulations prevail in the area of IT landscape. With the term IT compliance, we can describe compliance with the regulations in corporate management.
Compliance in itself merely means that the applicable legal rules and recognized social values and standards are always respected within the framework of all business activities.
In the light of the existing regulatory density for companies and entrepreneurs, cross-border activities, increasing regulation and in particular special liability for management bodies, each company must operate compliance management today.
Rechtsanwalt Dipl.-Ing. Michael Horak, LL.M.
Risk-related areas
In particular, the risk-related areas in each company must be identified and measures to reduce liability for the company and avoid liability in favour of the management body, in particular managing directors, executive board and supervisory board. The IT sector of a company is often one of the risk-ridden areas; IT companies themselves are active in a risky industry. IT outsourcing, cloud computing, and mobile services lead to even greater demands on IT compliance.
Management bodies
According to § 93 para. 2 AktG, the management bodies of a public limited company are personally liable for the violation of your organisational and supervisory obligations. This applies to (the) managing directors of a GmbH in accordance with § 43 para. 2 GmbHG i.V.m. § 93 para. 2 AktG.
We will gladly call you back.
The members of the governing bodies are responsible for their performance. In correlation with the industry and size of the company as well as its national or international orientation, liability risks increase both for the company and – in particular – for management bodies.
IT compliance organisation
The competent organization of regular conduct within the company and the proof of an IT compliance organisation are therefore at least advantageous for the following topics:
minimising the liability risks of the company and the personal liability of the management bodies; award of public and private contracts; creditworthiness, lending and conditions; prevention of criminal proceedings and irregularity; Going Public.
Contact us for a first consultation.
-
Antitrust proceedings: ECJ confirms acquisition by the EU Commission in respect of corporate restructuring
ECJ, Judgments of 1 October 2026, C-855/24 P (Crown Holdings) and C-845/24 P (Silgan Holdings) When the cartel investigation changes to the EU Commission Companies cannot rely on a trial that has been started at the Federal Cartel Office to be completed there. On 1 October 2026, the European Court of Justice confirmed that the European Commission had initiated antitrust proceedings under certain...
-
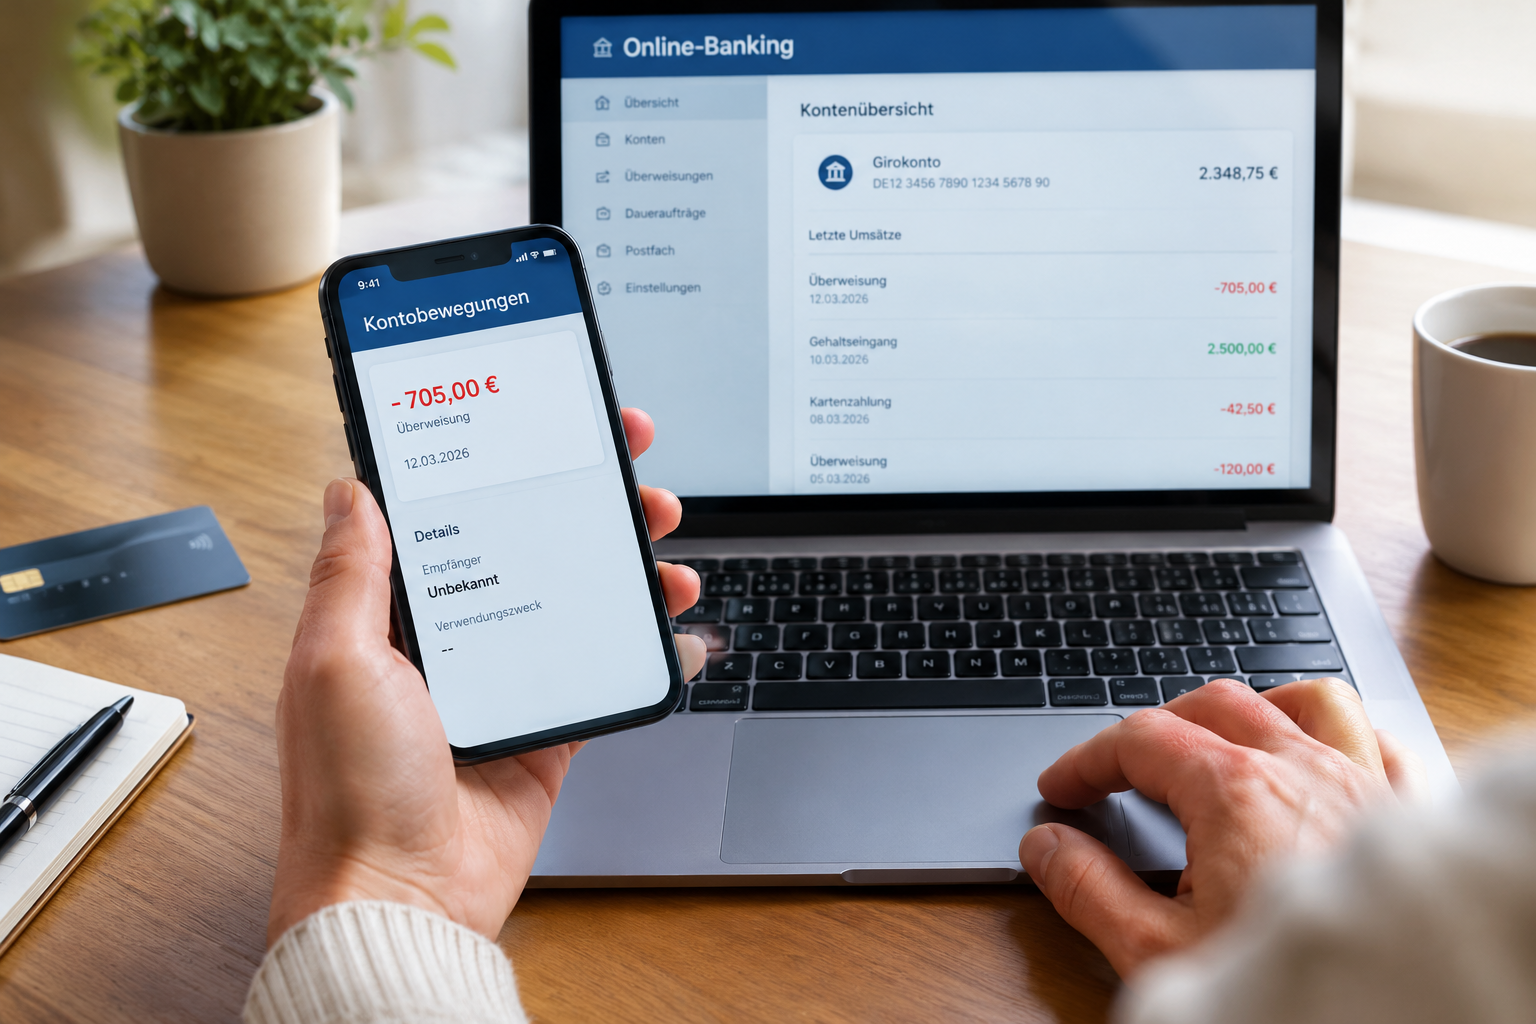
ECJ: Banks must first reimburse unauthorised debits for phishing victims
Judgment of the European Court of Justice of 15 October 2026 – C-70/25, Tukowiecka Banks and other payment service providers may not refuse or delay the reimbursement of unauthorized payment transactions solely because they accuse the customer of gross negligence. The European Court of Justice (ECJ) has clarified this in the case of Tukowiecka. The decision is particularly applicable to complaint management, fraud prevention and...
-
Searches 2026: Preparing reception, IT and management
On an unannounced official visit, employees need a short, achievable action plan. Clear contacts, factual documentation and the respect of the respective rights are crucial.
-
Cyber Resilience Act 2026: Organize Product Incidents and Notifications
Manufacturers of digital products need to work together on security incidents in both legal and technical terms. A prepared reporting process combines product knowledge, incident response and clear decisions.
-
AI-Compliance 2026: Controlled release of operational applications
An AI application can affect several legal areas at the same time. A release process must therefore consider the role, function, data and actual use.
-
Compliance Due Diligence 2026: Identifying risks before purchasing a company
Compliance risks influence purchasing decision, contract design and integration. A careful examination is based on the target company and its actual business relationships.
-
Award compliance 2026: evidence of self-cleaning
A breach of compliance can jeopardise participation in public procurement. Self-cleaning depends on the legal requirements and comprehensible measures.
-
Trade secrets 2026: Safeguards instead of flat-rate contractual clauses
Know-how protection begins with the question of which information is really confidential. Contracts, technical authorizations and operational procedures must jointly support this protection.
-
Antitrust 2026: Competition contacts at trade fairs and association meetings
An informal conversation can become relevant under antitrust law if competitors exchange sensitive information. Companies should prepare employees for specific interview situations and offer a reliable internal reporting route.
-
Internal Investigations 2026: From Suspect to Reliable Investigation Plan
In the case of conspicuous payments or concrete indications of misconduct, the procedure decides in the first days on the quality of the later information. Overburdened interviews and flat-rate data accesses can additionally burden the investigation.