
With IT compliance, the Corporate governance compliance with legal, internal and contractual regulations in the IT sector.
IT is an abbreviation and describes the technology for data processing. The abbreviation can also be described with information technology or information technology.
Priorities of IT compliance
information security, availability, data retention and Data protection are the focus of IT compliance. The priorities of IT compliance therefore first concern requirements that address the company's IT systems.
Purpose IT compliance
Finally, with compliance with rules, entrepreneurs want to increase IT security and benefit from better company assessment.
The implementation of compliance is not a short-term measure, but an always ongoing realization.
Rechtsanwalt Dipl.-Ing. Michael Horak, LL.M.
Penalties for IT compliance violations
From EU directives to international conventions to company-internal conventions and commercial practices, IT compliance includes numerous regulations. If an undertaking fails to comply with these legal obligations, it will face high fines and liability obligations.
We advise you on IT compliance.
Managing directors and board members are responsible
Managing directors and board members of public limited liability companies (AG) and limited liability companies (GmbH) are personally liable for compliance with the statutory regulations. Civil and even criminal sanctions threaten violations. The Federal Data Protection Act provides for penalties in the event of infringement (§ 44 BDSG) from the fine to two-year imprisonment.
Financial institutions are required to carry out audits, which means that they are practically forced to implement the IT compliance.
In the basic protection catalogues of Federal Office for Information Security (BSI) find companies comprehensive instructions for action.
National and international IT compliance rules
The following are the most important rules on national and international IT compliance:
Germany
- Federal Data Protection Act (BDSG)
- Law on control and transparency in the business sector
- Digital Tax Verification (GoBD): Principles for the proper keeping and storage of books, records and documents in electronic form as well as data access
- Requirements of the Bundesanstalt für Finanzdienstleistungsaufsicht (BaFin) for the banking sector: Minimum requirements for risk management (BA) (MaRisk, for short)
- Telecommunications Act for Germany
Austria
- Telecommunications Act for Austria
European Union
- General Data Protection Regulation (EU GDPR)
- Requirements from the Basel III framework for the banking sector: Capital Requirements Directive and Capital Adequacy Regulation
- Financial Market Directive: Directive 2014/65/EU on markets in financial instruments
United States
European companies listed on the stock exchange in the United States are obliged to comply with the Sarbanes-Oxley Act (SOX).
International
International regulations are also the following:
- HIPAA
- International Financial Reporting Standards (IFRS)
- Payment Card Industry Data Security Standard (PCI-DSS)
From a seminar for beginners to training on the way to Compliance specialist we offer different levels.
-
Compliance 2026 – What you need to know today
Compliance law covers many areas. In 2026, compliance is not only a legal obligation but also a competitive factor. Key topics include: Data protection and IT compliance: As digitalisation progresses, companies must ensure that the processing of personal data is lawful. DSGVO obligations include, as well as secure data transmission, access rights, data retention and reporting requirements for data protection violations. Antitrust and competition law: companies...
-
The IT compliance is legal
Just call us. We are happy to advise you. Legal, internal and contractual regulations prevail in the area of IT landscape. With the term IT compliance, we can describe compliance with the regulations in corporate management. Compliance in itself simply means that the applicable legal rules and recognized social values and norms within the framework of all corporate...
-
Avoid attacks by Trojans, viruses or cyber attacks
From a seminar for beginners to training on the path to becoming a compliance specialist, we offer various levels. Anyone who has ever experienced a system failure or suffered a data loss knows how vulnerable we have become during our daily work in the office, in production and on the road. Increasing attacks on corporate networks show the extent to which...
-
Kaizen meets compliance
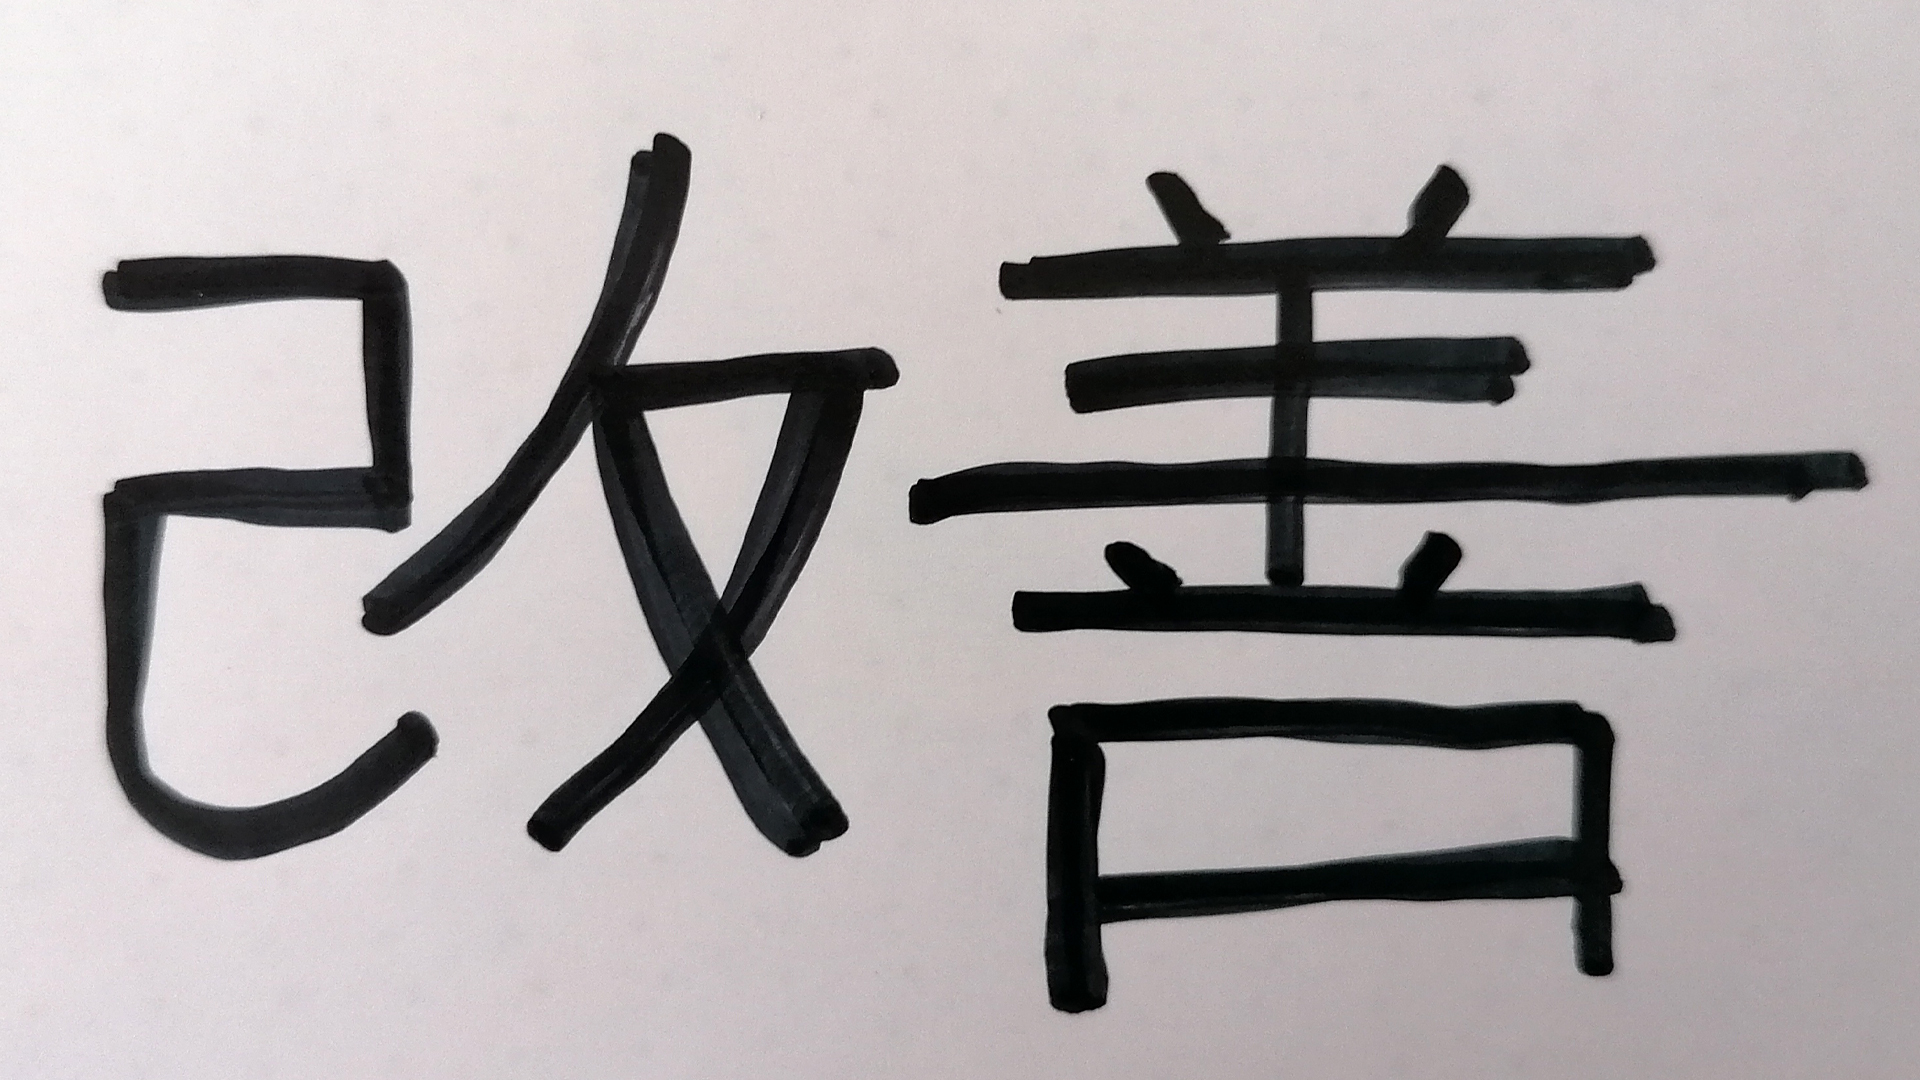
If there is a great willingness to change, management can apply the Kaizen principle. Kaizen means continuous improvement of all corporate functions, including processes, products and services involving all employees and managers. Kaizen is an important Japanese management concept. Compliance in constant change Steady change lies in the nature of compliance. Jurisdictions in the field of data protection or...
-
Death sin 7: rejecting key technologies

The market offers a wealth of technologies for compliance requirements. Legal and compliance departments are responsible for the procurement of these technologies. IT managers can, however, participate in the selection and use of optimal solutions. Use a first IT compliance consultation. Essential Technology Areas The essential three technology areas in which compliance managers should invest are: 1. Basic Systems of Record...
-
Deadly Sin 6: Compliance dictates IT Security
Managers in the field of IT security depend on them to be always up-to-date with the legal requirements for compliance. However, you must not lose sight of a stable safety program. A good data flow, a thriving company that remains competitive – that succeeds with the right attitude. Lawyer Dipl.-Ing. Michael Horak, LL.M. Security program...
-
Deadly Sin 5: There Is No Understanding of Regulation
In IT-related issues such as data protection, confusion may arise in the absence of a regulatory understanding within the company. This is due to our experience that understanding a company for a legal point of view often does not coincide with the intention of a regulation. Understanding The result is that companies don't know what regulators want from them. Companies should...
-
Death Sin 4: Governance Structure Missed
Although companies control basic processes and controls, our experience often lacks governance structure. A good governance structure is designed to ensure risk coverage as well as the adaptation of their processes and controls to regulatory requirements. We are happy to advise you in IT compliance. Effects of a lack of governance structure Impacts of a structurally-free compliance governance can be the following: The corporate architecture becomes sluggish. Reactions to...
-
Death Sin 3: Preparing a Bad Working Group
Knowledge, skills, experience – too little of it in a working group brings problems. A Chief Information Officer (CIO) should necessarily create a highly qualified Compliance Working Group. Insufficiently prepared teams can even be risky. The CIO is responsible for the strategies in the fields of information technology (IT) and computer systems with the aim of achieving the objectives of the...
-
Death Sin 2: Excluding Exceptions
Bypassing the compliance rules can be risky. Sometimes, however, it is necessary to make exceptions and disregard the rules. In order to avoid any risk, you should therefore take precautions. We also advise you on compliance risks. Exceptions take into account exceptions in the compliance process, can be a very wise strategy. And that's...